
NO.0x0001
- people have completed this challengeContributors:
🔗 WalletConnect Session Hijack 🔗
You scanned a QR code months ago. The session is still open. Who is on the other end?
Step 1 · Audit your connected apps
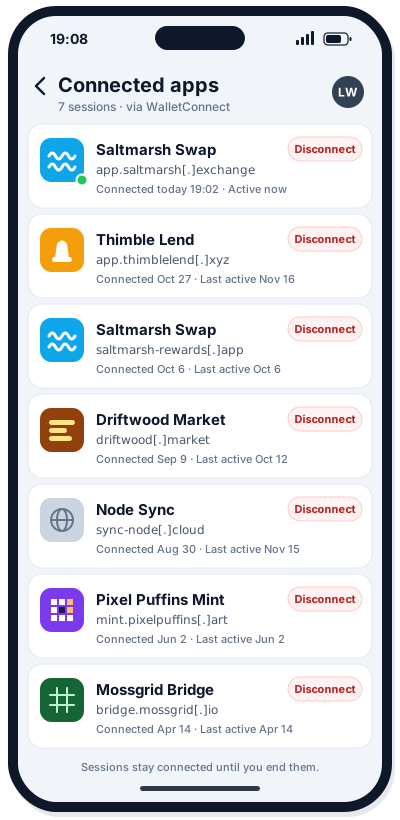
19:08. You are mid-swap on Saltmarsh Swap when you open the “Connected apps” screen in Limpet Wallet for the first time in months. Seven live WalletConnect sessions. Whoever holds the other end of each one can push a request to your phone at any moment.
Tap a session on the phone to inspect it, then disconnect it or leave it. Finish the audit when you are happy with the list.
Saltmarsh Swap
app.saltmarsh[.]exchange- Connected
- Today, 19:02
- Last activity
- 2 minutes ago
- Chains requested
- Ethereum, Arbitrum
- Methods it may request
eth_sendTransactionpersonal_signeth_signTypedData_v4
What you remember: You opened the site from your own bookmark and scanned the QR shown on your own laptop. Your swap is waiting to confirm.
You are mid-swap here, so this one stays. You will disconnect it the moment the swap confirms. Promise.
Idle sessions disconnected: 0 / 6