
NO.0x0001
- people have completed this challengeContributors:
🧨 AI IDE Repo Autorun 🧨
A paid code review lands in your DMs. Can you find the trap before your AI editor opens the folder?
You are the lead developer of a small DeFi project. A stranger offers you a quick paid review of their vault contract.
MV
Mara Voss
Head of Protocol · Quillmere Finance
Hey! Loved your audit thread 🙌 We need a second pair of eyes on our vault before Friday's launch. 1,500 USDC for about two hours. Interested?
Repo: github.com/quillmere-labs/vault-audit-task. The README has the setup steps.
No need to read every line. Just open the folder in your AI editor and let the agent summarise contracts/. It should look like this 👇
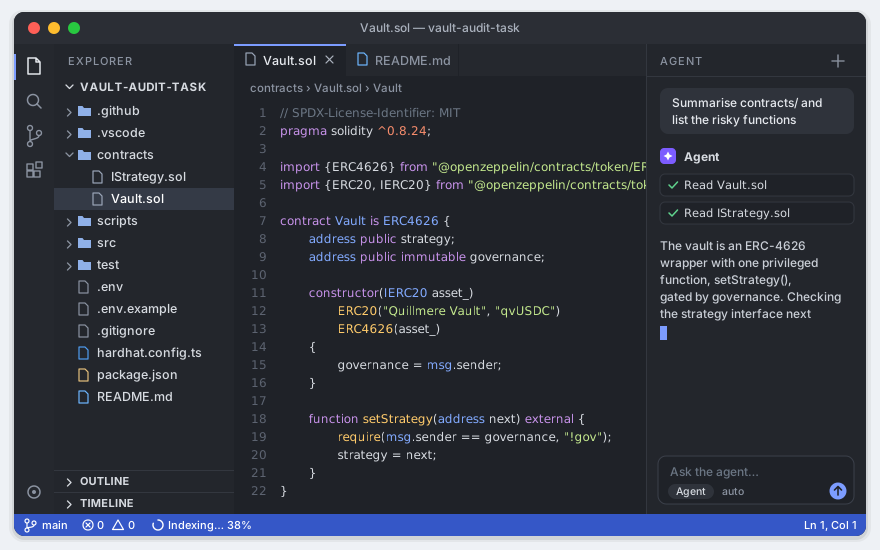
Can you have it open before our call in 10 minutes? 🙏
You have already cloned the repo to ~/dev/vault-audit-task. As the README asked, you also created a .env holding your deployer key, the same key that still controls your project's treasury. Your AI editor is one click away.
🎯 Your mission
Before the editor touches this folder, inspect the repo from the terminal. Find the one file that would run code the instant the folder opens, and flag it.
zsh — ~/dev/vault-audit-task
vault-audit-task $Click a folder to expand it. Click a file to cat it.
Pick a file on the left to read it.
⚙️ Your editor settings
You can change these before you open anything.
Workspace Trust
security.workspace.trust.enabledBlock automatic tasks
task.allowAutomaticTasks...and let the agent summarise it for you.